GitLab
Latest versionA web-based DevOps lifecycle tool that provides a Git repository manager providing wiki, issue-tracking, and CI/CD pipeline features.
Authentication DetailsComposio-managed OAuth available
Frequently Asked Questions
How do I set up custom OAuth credentials for GitLab?
Use your own GitLab OAuth application when you want users to see your app's name on the consent screen, or when you connect to a self-managed GitLab instance.
Create the GitLab app
-
Sign in to GitLab, click your avatar in the top-right corner, and select Edit profile.
-
In the left sidebar, click Applications (direct link on GitLab.com:
https://gitlab.com/-/profile/applications). On a self-managed instance, use the same path on your own host.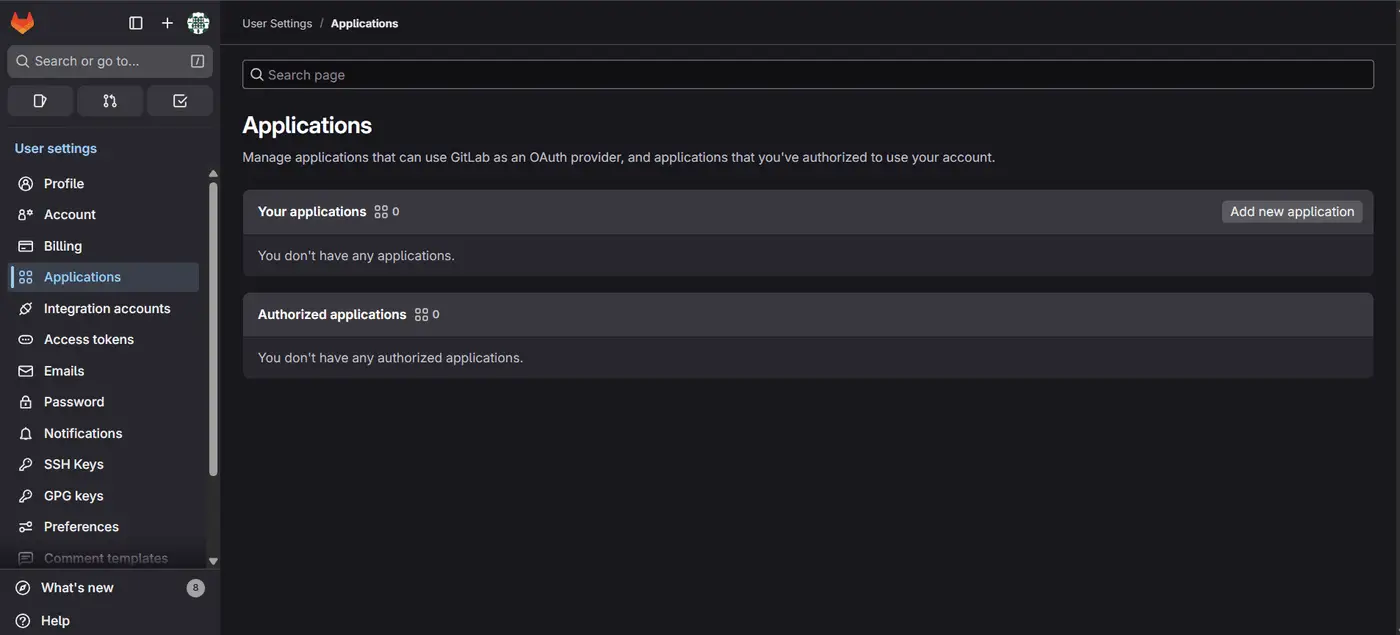
-
Click New application and enter a name, such as
Composio GitLab Integration. -
In Redirect URI, paste
https://backend.composio.dev/api/v1/auth-apps/addwith no trailing/. It must exactly match theoauth_redirect_urifield in your Composio auth config.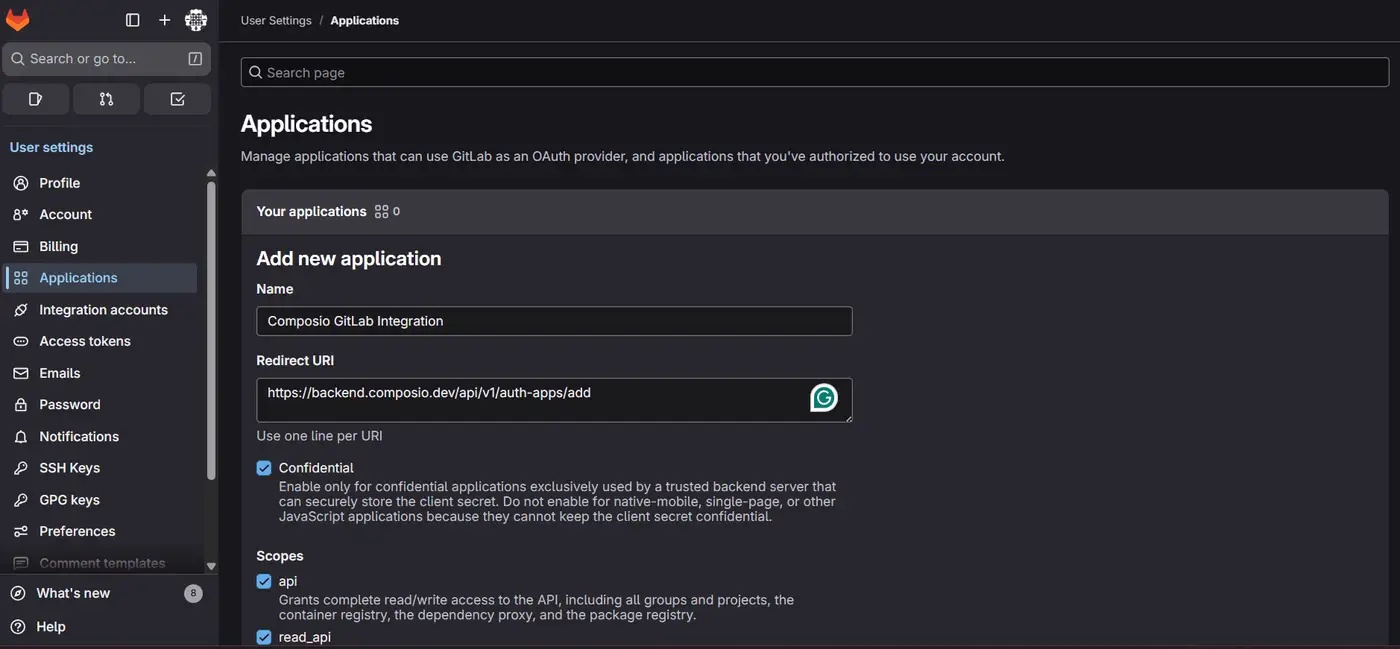
-
Select the scopes your integration needs, then click Save application.
-
Copy the Application ID (your Client ID) and the Secret (your Client Secret). GitLab shows the secret only once.
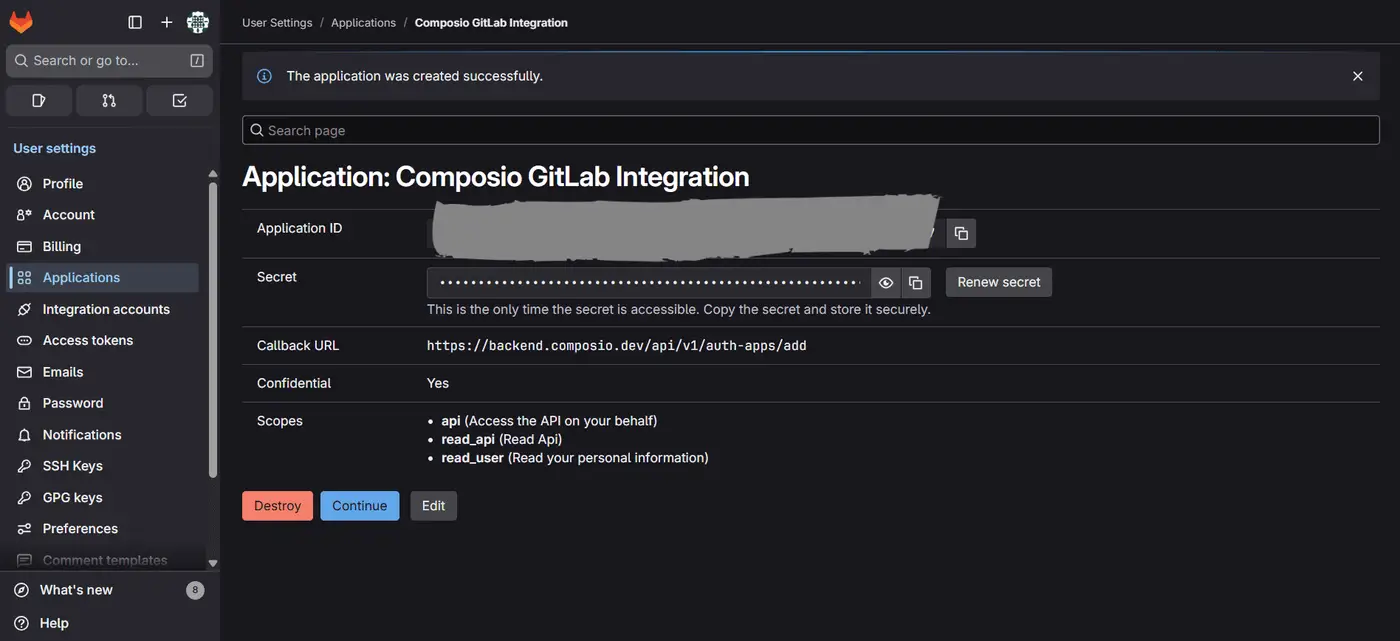
Create the auth config in Composio
-
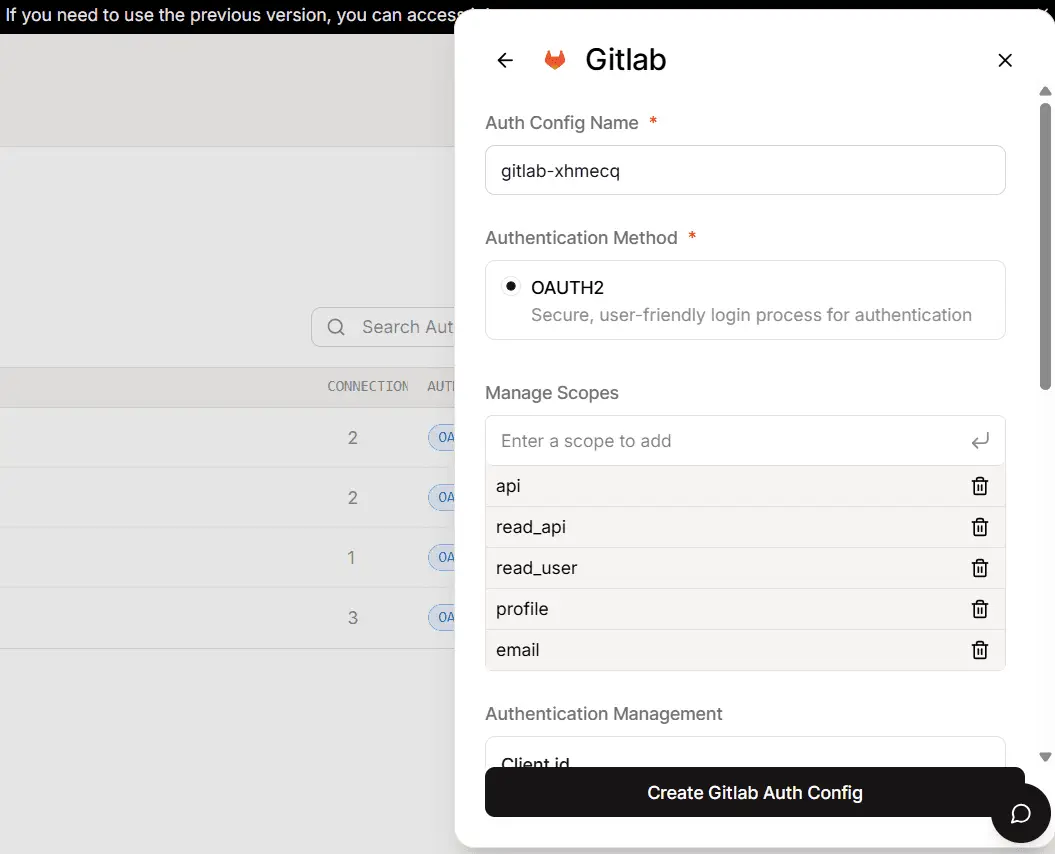
In the Composio dashboard, go to Auth Configs, click Create Auth Config, and select GitLab.
-
Set the authentication type to OAuth2 and choose Use your own developer authentication.
-
Paste the Application ID as Client ID and the Secret as Client Secret. Add the same scopes you selected in GitLab, then click Create GitLab Auth Config.
-
Click Connect Account, approve the permissions on the GitLab consent screen, and confirm the account shows as Active.
See Custom auth configs for the general flow.
Scopes
The default auth config requests api, read_api, read_user, read_repository, write_repository, profile, and email. api grants full read/write API access; use read_api instead for read-only access. Select only the scopes you need in the GitLab app and use the same list in the auth config.
Self-managed GitLab
The OAuth2 auth config has two URL fields:
full: your GitLab server URL with/api/v4appended. The default ishttps://gitlab.com/api/v4.authorizationUrl: your GitLab server URL without the API path. The default ishttps://gitlab.com.
For a self-managed instance, create the OAuth application on that instance and set both fields to your instance's URL, for example https://gitlab.example.com/api/v4 and https://gitlab.example.com.